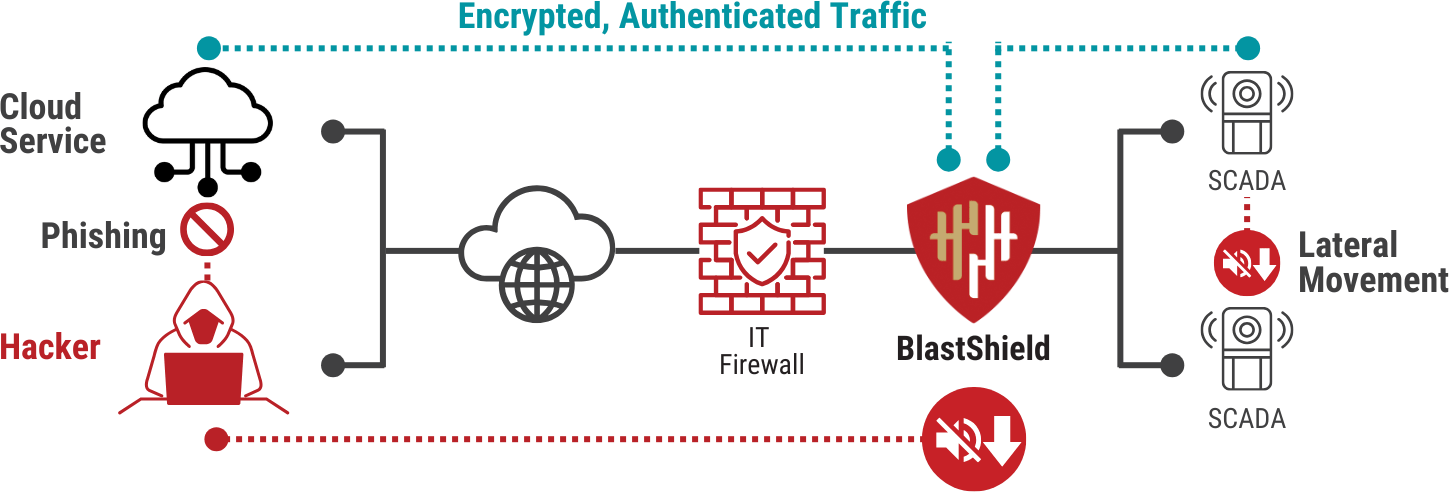
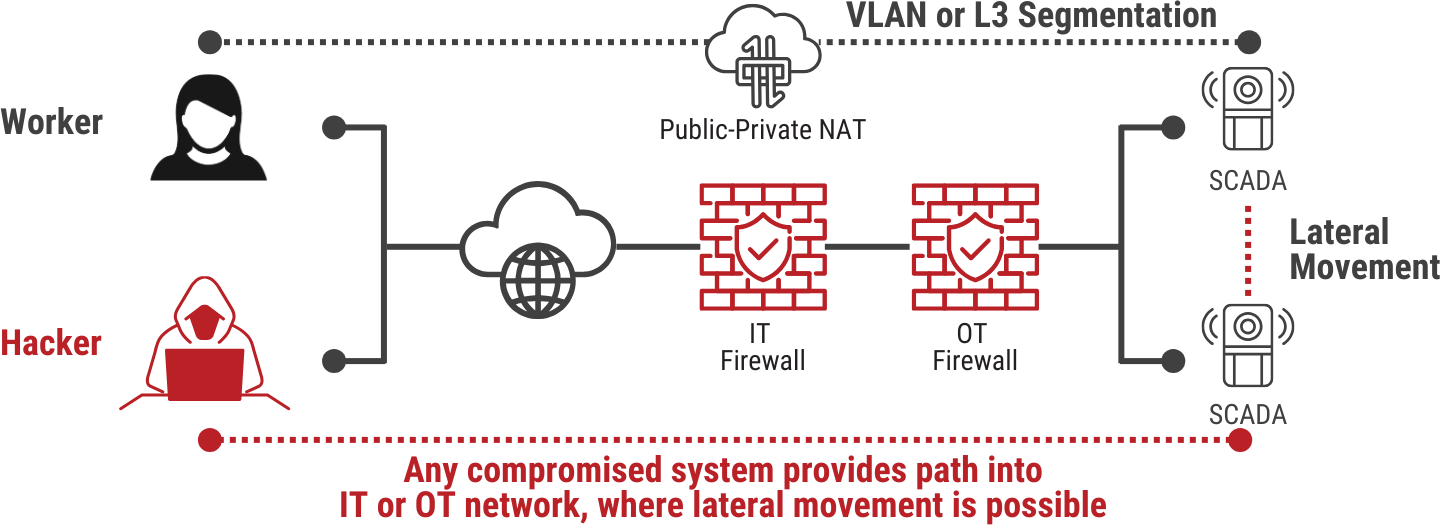
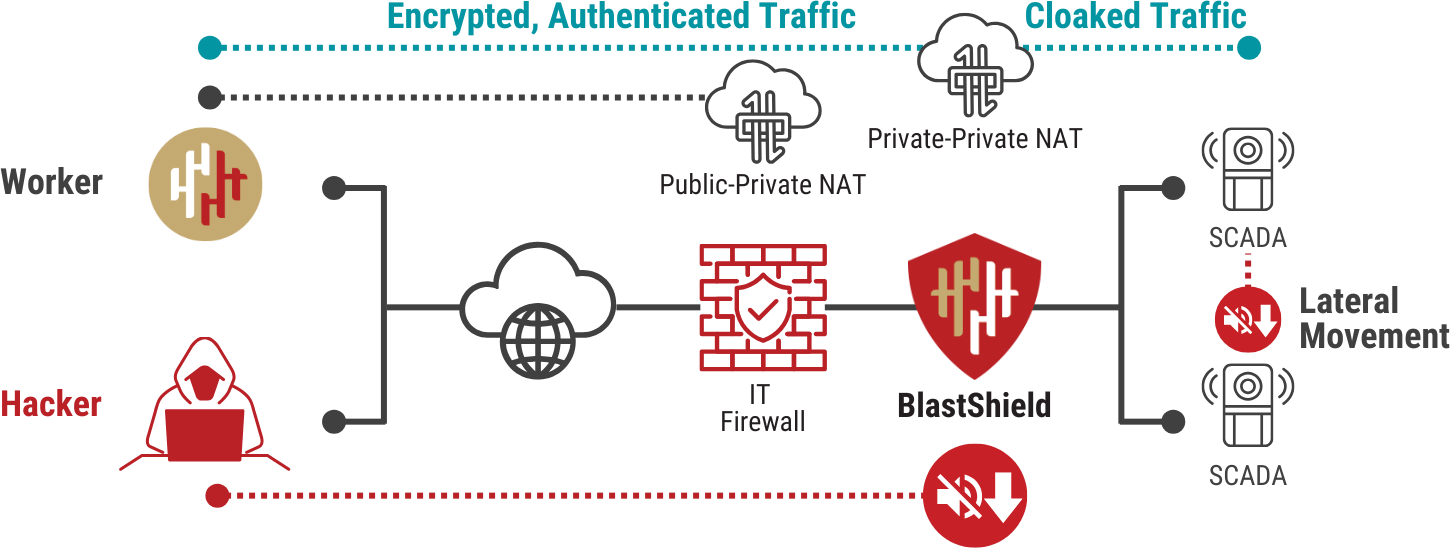
Network cloaking silently drops every packet that is not cryptographically authenticated. Your PLCs, RTUs, HMIs, and unpatchable legacy devices stop responding to scans, probes, and automated reconnaissance. To an attacker, your OT network looks like empty address space.
See a Live Port Scan Return Nothing20 minutes. Live environment, not slides. Our engineers run the scan while you watch.
What is network cloaking?



Network cloaking makes critical OT systems invisible to unauthorized users. They cannot attack what they cannot see. With network cloaking active, any connection that is not cryptographically authenticated is silently dropped.
That last word carries the meaning. A cloaked device does not refuse the connection or send a reset. It does not answer at all. There is no banner to read, no open port to fingerprint, and no response timing to analyze. A scan against a cloaked network returns exactly what a scan against unused address space returns: nothing.
This is what makes cloaking particularly useful for operational technology. OT networks run on equipment that stays in service for decades, often past vendor support, frequently unpatchable, and sometimes so fragile that a ping sweep can take it offline. You cannot patch your way out of that. Cloaking takes a different approach: it removes the device from the attack surface without touching it.
An unpatched PLC that responds to a scan is exploitable. A cloaked one is not there to be attacked.
In search engine optimization, cloaking is the practice of showing search engine crawlers different content than human visitors see. It is a deceptive practice; it violates Google's spam policies and can get sites removed from the index.
In network security, cloaking is the opposite of deception. Nothing is shown to anybody. A cloaked asset does not respond to unauthorized traffic at all, so there is no content, real or faked, for anyone to receive.
The two share a word and nothing else. This page is about the network security meaning: making industrial control systems unreachable and undiscoverable to anything that has not authenticated first.
Related but distinct: SSID cloaking hides a wireless network name while the network still broadcasts and responds. IP cloaking usually refers to masking an origin address in advertising or affiliate traffic. Neither removes an asset's response to a scan.
Network cloaking inverts the default behavior of a network. Instead of responding to traffic and then deciding whether to allow it, a cloaked network stays silent until the requester has already proven who they are.
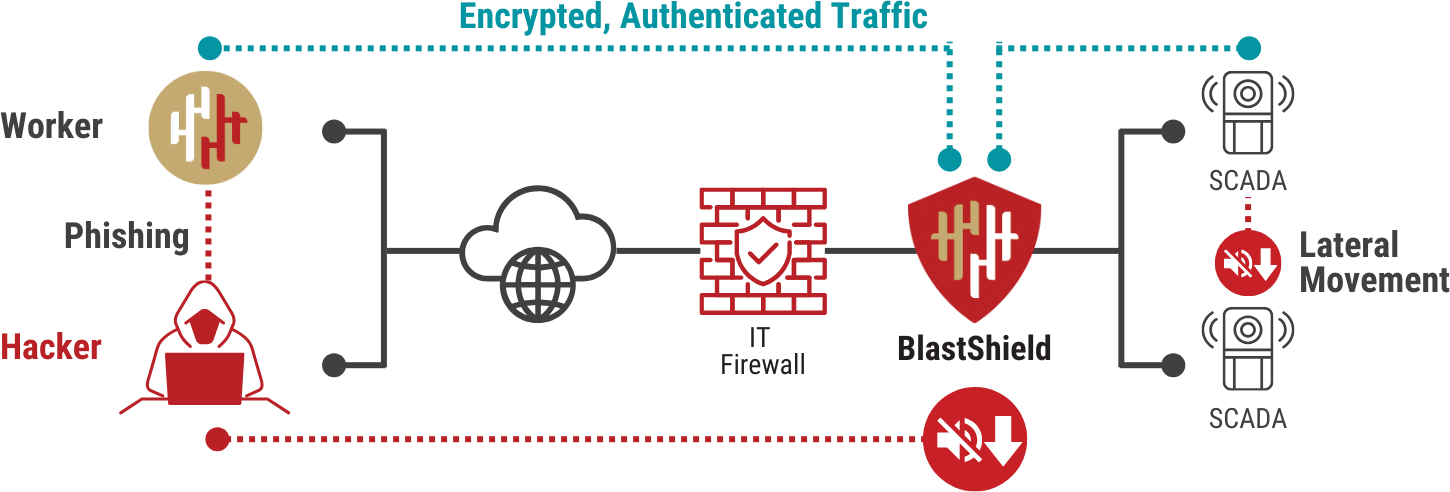
Any packet arriving without valid cryptographic authentication is dropped without a response. Nothing in the exchange reveals that anything is listening.
Authorized users authenticate first, using passwordless, phishing-resistant multi-factor authentication: QR challenge-response, local biometrics, and a device keystore. Because there is no password in the flow, there is no password to steal, phish, or replay.
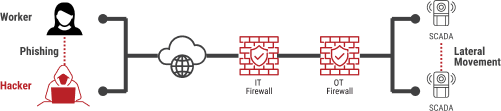
Once authenticated, a user reaches only the systems their policy permits. Everything else stays cloaked, including from users already inside the network. This is what blocks east-west lateral movement after a device is compromised.
OT traffic crossing the BlastShield boundary travels in peer-to-peer encrypted tunnels. Legacy OT protocols that offer no native encryption are protected in transit without modification.
External scans see empty space, internal attackers can reach only what the compromised identity was authorized to access, and legacy devices remain reachable by the operators who need them, but not by anyone else.
Several vendors now market some form of asset hiding. That is a real shift, and the useful question is no longer whether a product claims to be invisible. It is where the concealment comes from, because that determines what happens when the network changes.
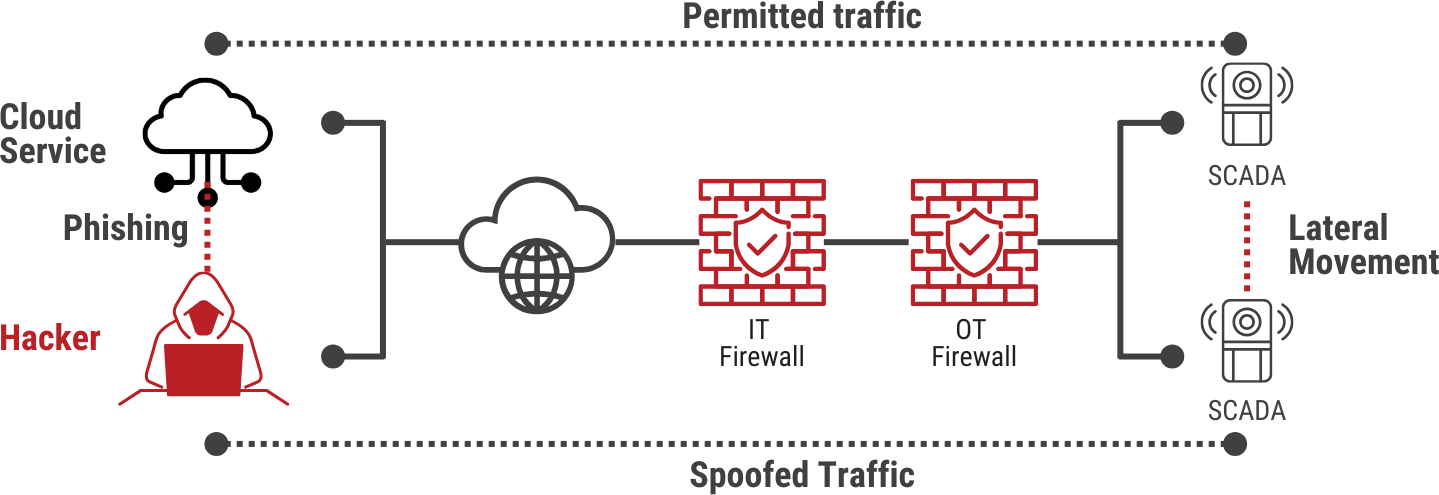
Concealment as a property of topology. The common approach is to place an appliance in front of the asset. Traffic that crosses the appliance is filtered; the asset behind it is concealed. This works, and it is a genuine security improvement. But the concealment belongs to the box and its position in the network. It holds for as long as every path to the asset crosses that box.
Concealment as a property of the asset's own policy. BlastShield binds the cloaking policy to the protected asset's cryptographic identity rather than to a location in the topology. On hosts that can run software, the BlastShield Agent enforces the policy at the asset itself, accepting connections only from verified clients. For devices that cannot run any software, which is most of the OT estate, the BlastShield Security Gateway performs authentication and access control on the device's behalf. In both cases, the policy travels with the asset and its identity.
Three questions separate any two products in this space:
CrowdStrike's 2026 Global Threat Report found that 40% of vulnerabilities exploited by China-nexus adversaries targeted edge devices that lack comprehensive monitoring. An appliance that must be reachable to work is one that can be found and attacked.
In its 2026 Market Guide for CPS Secure Remote Access, Gartner recommends that organizations avoid products that require inbound connections to be enabled, and identifies "shadow access" as a critical blind spot: undocumented remote connections that bypass corporate firewalls and permeate CPS environments.
In the December 2025 attack on Polish distributed energy resources, in which Russian attackers reached more than thirty small wind and solar generators and control equipment at a combined heat and power plant, forensics determined the attackers held administrative privileges on the firewalls deployed at each affected site, having gained access months earlier.
CrowdStrike recorded an average eCrime breakout time of 29 minutes in 2025, a 65% year-over-year improvement, and a fastest recorded breakout of 27 seconds. OT patch cycles are measured in years, and for a controller installed in 2009, never.
In January 2026, the UK NCSC and nine international partners published Secure connectivity principles for Operational Technology, a 33-page document focused on networks and connectivity rather than endpoints. Its Principle 2 is "Limit the exposure of your connectivity," and its Principle 5 is "Harden your OT boundary."
Gartner, Market Guide for CPS Secure Remote Access, Katell Thielemann, Wam Voster, et al., 3 February 2026.
GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.
Gartner does not endorse any vendor, product or service depicted in its research publications and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner's research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
These terms get used interchangeably. They describe different things.
Obfuscation and moving-target defense aim to confuse reconnaissance. Cloaking starves it. For a network full of devices that will never be patched, confusing an attacker buys time; removing the device from view removes the target.
Our engineers will run a live port scan against a BlastShield-protected network while you watch, and show you what Shodan and Nmap return. No slides. No prerecorded video. 20 minutes.
With cloaking active, BlastShield fails closed. Protected assets stop answering. That is a security property, and in OT it is also an availability question, so the two answers go together: deploy redundant Gateways, and ensure that already-established sessions are retained during failover, so live sessions do not drop. If the Orchestrator is unreachable, the Gateway continues enforcing the policy it already holds. The Orchestrator is the policy plane, not the data path, and it can itself be made redundant on-site, in the cloud, or both.
BlastShield blocks and logs any connection attempt from a system that is not explicitly configured with a policy. This bounds the consequence of an incomplete asset inventory: an asset your inventory missed is denied the moment it tries to communicate, and the log becomes a record of exactly what the inventory missed.
BlastShield does not perform active asset discovery. It records what attempts to communicate. It does not enumerate what sits silent. Where full discovery is required, that is a separate capability.
Operators define and enforce authorized communication pathways. A compromised device attempting to transmit to an unauthorized external destination is blocked. Dormant malware already resident inside the network cannot reach external command infrastructure.
Both failed and permitted access attempts are logged, as are configuration changes. Retention is configurable, and logs export via local storage, API, syslog streaming, or CSV over FTP. The policy configuration itself can be exported, saved, and reapplied.
The Orchestrator has no formal policy approval workflow. If a user's permissions allow a policy change, that change takes effect immediately. Control is by permission model plus an after-the-fact configuration change log, not by two-person review. Any separation-of-duties requirement must be enforced through the permission model or your own change management procedure.
PLCs, RTUs, sensors, and controllers that cannot be updated stop appearing in scans. The vulnerability remains; it is no longer reachable.
Protecting legacy OT devices →Attacks begin with mapping the network. Cloaking removes the map.
Preventing reconnaissance →A zero-day needs a reachable target. An unknown vulnerability in a cloaked device has no path to reach it.
Automated reconnaissance depends on responses to analyze. Cloaked networks return none, so the automation has no input.
Protection against AI-powered attacks →Access is scoped to the authenticated identity. A compromised device reaches only what that identity was authorized to reach.
Segmenting flat networks →Passwordless, phishing-resistant MFA removes the credential as an attack vector. There is no password to capture.
Phishing-resistant OT remote access →Contractors connect to specific authorized systems, not to the network. Everything else stays invisible to them.
OT secure remote access →Thousands of legacy PLCs, IEDs, and RTUs stay in service for decades without vendor support, and continuous monitoring rules out air gapping. Cloaking places them behind an authenticated boundary without changing existing network architecture.
Flat networks and shared credentials mean one successful phishing attempt can reach everything. Cloaking removes external visibility of pumps, sensors, and PLCs and scopes internal access to authorized identities.
Ransomware reaches the production line through stolen credentials and unpatched OT. Cloaking removes both paths.
Some transmission systems are fragile enough that a ping sweep can take them offline, so they must be shielded from external traffic while remaining monitorable internally.
Building automation, HVAC, and power management are the soft path into a facility customers depend on.
A BMS interfaces with every automated system in the building and connects externally for remote access.
In 20 minutes, our engineers will scan a BlastShield-protected network live, show you what Shodan and Nmap return, and walk through what cloaking your environment would involve. First principles and architecture, not buzzwords. If it is not a fit, we will say so.
Network cloaking makes critical OT systems invisible to unauthorized users. They cannot attack what they cannot see. With network cloaking active, any connection that is not cryptographically authenticated is silently dropped.
Traditional firewalls control access with predefined rule sets but still expose network topology and device presence through open ports and predictable traffic patterns. Network cloaking actively conceals the network infrastructure itself, so attackers cannot identify potential targets in the first place.
Yes. Zero-day vulnerabilities are unknown exploits that attackers can leverage before patches are available. Network cloaking provides a proactive defense by making vulnerable devices undiscoverable — even if a zero-day exploit exists, the attacker cannot find a device to use it against.
Yes. Many OT environments rely on legacy systems that cannot be easily updated or patched. Network cloaking removes these devices from the attack surface entirely, preventing attackers from exploiting their outdated security features.
AI is increasingly used in cyberattacks to automate reconnaissance and identify vulnerabilities. Network cloaking counters these attacks by rendering the network invisible to automated scanning tools and AI algorithms — their reconnaissance simply returns no results.
Any sector that runs operational technology: oil and gas, water and wastewater, manufacturing, energy, data centers, and building management all use network cloaking to hide unpatchable legacy devices, reduce their attack surface, and keep critical operations running.
No, and they are unrelated. SEO cloaking shows search engines different content than human visitors see, a deceptive practice that violates search engine spam policies. Network cloaking in security shows nothing to anybody: an asset that has not been authenticated receives no response at all.
No. Obfuscation makes a network harder to interpret using non-standard ports, renamed banners, or decoy topology, but the network still responds. A patient attacker can work through obfuscation because the signals remain. Cloaking removes the response, so there is no signal.
Moving target defense rotates IP addresses, ports, or routes so that reconnaissance data goes stale before it can be used. It increases the attacker's cost, but the network remains visible. Cloaking makes the asset undiscoverable in the first place and requires no rotation, which fragile OT systems may not tolerate.
BlastShield deploys as a software overlay in front of protected assets, as a VM, a container, or a certified appliance, without changing the underlying network architecture. No agents are required on the protected devices, and no firmware changes are needed. It fails closed, so redundant Gateways are part of a production design, and established sessions are retained through failover.
An independent benchmark conducted by The Tolly Group measured BlastShield at 2.5 Gbps client-to-application across three concurrent clients, achieving throughput up to 34 times that of a comparison product in the same test set.
It is blocked and logged. BlastShield denies any connection attempt from a system not explicitly configured with a policy, and records the attempt. That log records what your asset inventory missed. BlastShield does not perform active asset discovery; it records what attempts to communicate, not what sits silent.
A practical process for making OT systems invisible to attackers: inventory exposed assets, deploy the BlastShield Security Gateway, enable cryptographic authentication, enroll users with passwordless MFA, and verify that cloaked devices no longer appear in scans.
Want to see steps one and five run against a live environment? Schedule a demo →